ANDROID BUDGET APP PRIVACY
Prepare a Phone for Temporary Sharing
Minimize finance exposure before handing an unlocked Android phone to another person.
01 / CONTEXT
Define the control decision
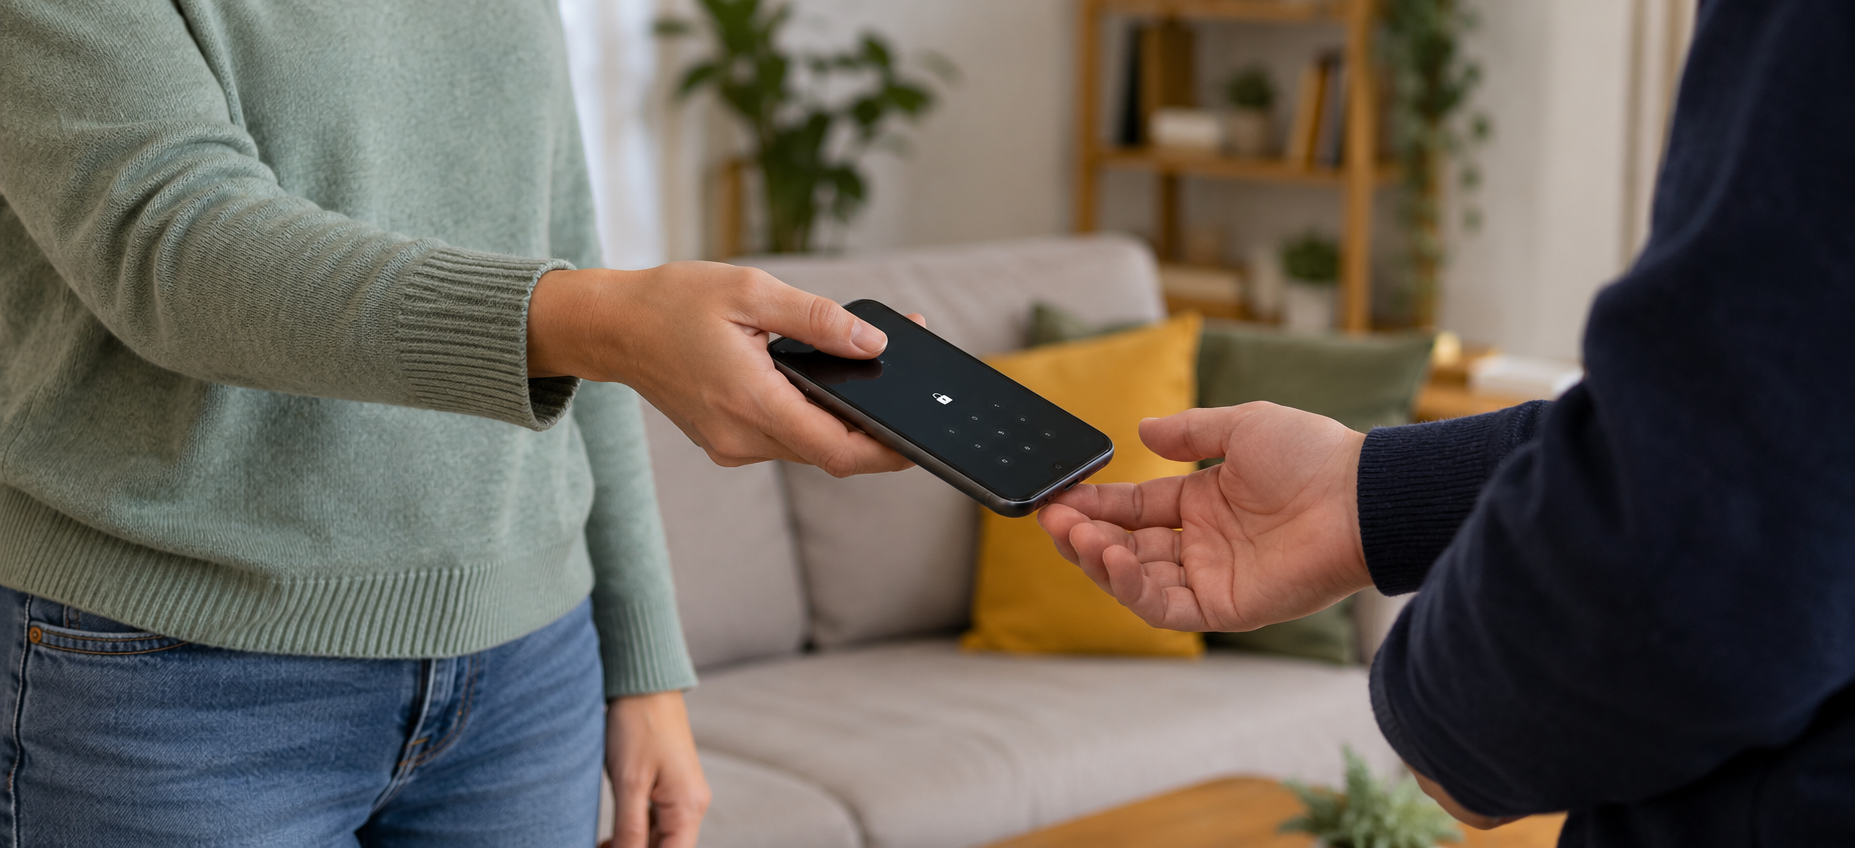
A friend, child, technician or colleague may need one phone function without needing access to transaction history. App entry protection is only one part of a deliberate handoff that also addresses notifications, recent apps, downloads and browser sessions.
Minimize finance exposure before handing an unlocked Android phone to another person.
02 / PROCEDURE
Run the control sequence
- 01
Close the finance app and clear sensitive recent-app previews.
- 02
Disable or minimize finance notification previews.
- 03
Use Android guest, app pinning or another supported handoff mode when available.
- 04
Test the locked finance app with a harmless demo profile.
- 05
Recheck account sessions, downloads and notifications after return.
03 / EVIDENCE
Preserve proof without personal data
A defensible privacy record identifies the phone owner, Android version, budget apps, sensitive screens, device-lock state, app authentication, secondary-lock configuration, notification exposure, backup behavior, recovery owner and next review date. It should not contain real balances, transactions, account numbers, credentials or personal notes. Use a fictional demo profile during every technical test.
Recheck the arrangement after changes to Android, the finance app, App Lock, device security, notifications, biometrics, cloud backup, account recovery, permissions or shared-phone routines. Confirm both usability and recovery: the owner should enter the finance app when authorized, another phone user should meet the intended barrier, and the owner should recover access without depending on undocumented steps. Preserve unexpected behavior before changing controls.
Keep the claim narrow. A tested entry lock may reduce casual access to one Android application, but it does not encrypt the device, secure the finance account, approve transactions, hide every notification or recent-app preview, detect malware, govern cloud copies, erase exports or guarantee recovery. Escalate those requirements to the Android, finance-provider and account-security controls designed to meet them.
Ask a second tester to follow the written privacy procedure with fictional data. Record whether that person can identify sensitive screens, test the locked entry point, recognize notification exposure, find the recovery owner and explain what remains visible elsewhere. This usability check reveals hidden shortcuts, ambiguous recovery steps and unsupported assumptions before a phone, Android, finance-app or account change.
04 / BOUNDARY
State what the control cannot prove
An app lock cannot prevent screenshots taken before handoff, browser access, notification leakage, malicious software or disclosure through another synchronized device.
Validate the exact Android version, device lock, finance-app authentication, notification settings, backup behavior and current App Lock release. If device encryption, account security, transaction authorization, malware protection, cloud-backup control or guaranteed recovery are required, select systems designed for those jobs rather than broadening a desktop restriction claim.
05 / SOURCES
Primary references
References support specific controls and do not imply endorsement.